La documentation est disponible en anglais.
Documentation / Use cases
PII protection
Detect and redact sensitive spans before they reach the LLM provider. Essential for support agents, CRM copilots, and regulated demos.
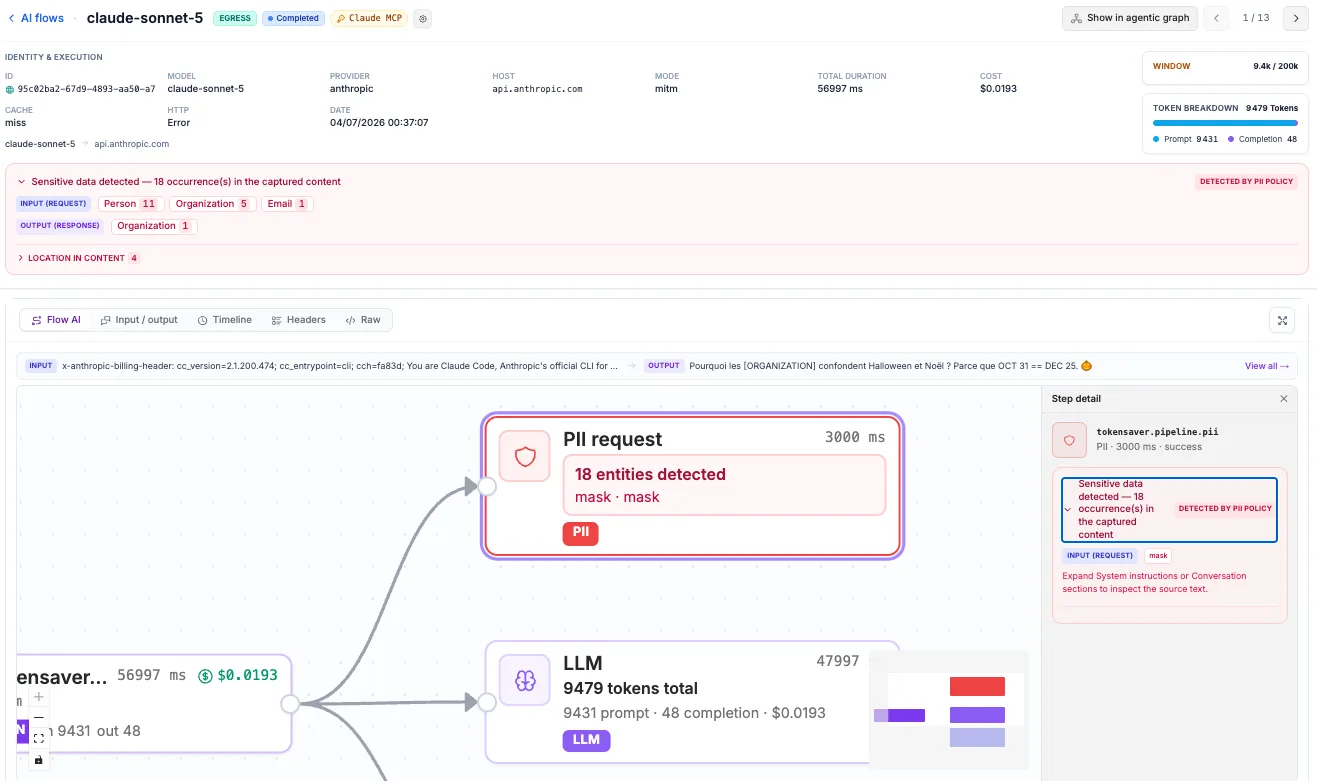
PII runs as a pipeline module. When enabled on the key, prompts are scanned; detections are audited on Flux IA (and visible on the agentic graph for sensitive runs) so compliance can see that filtering happened without reading raw secrets in every log.
- User text
- PII detect / redact
- Safe prompt
- LLM provider
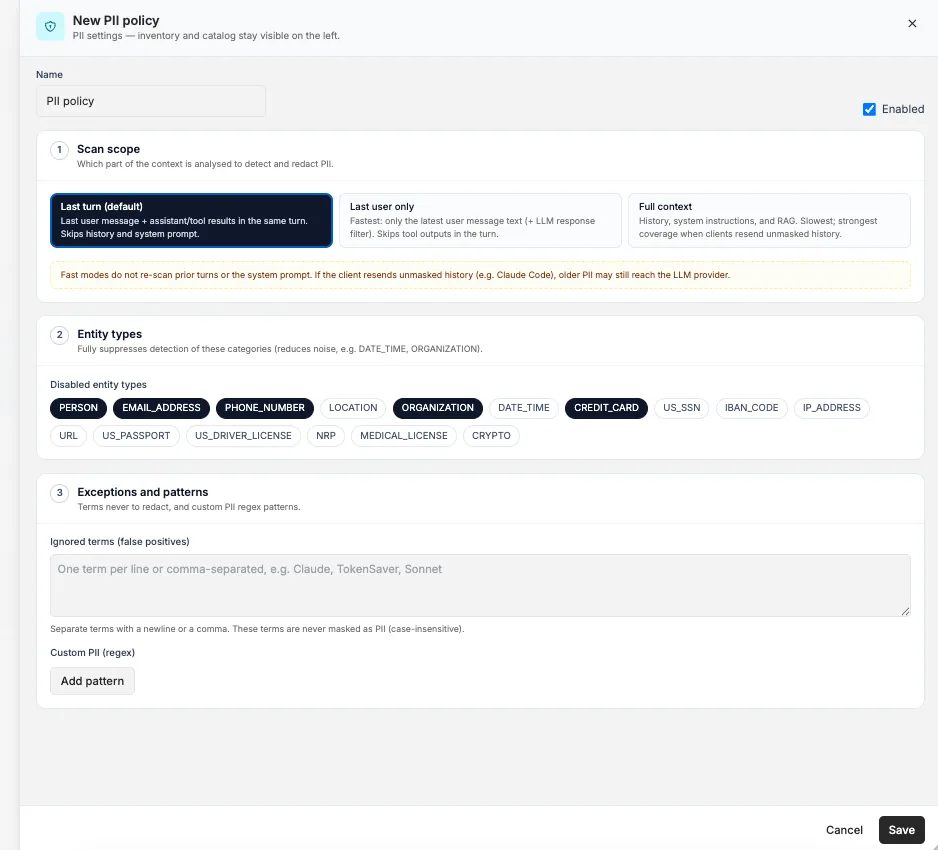
- Enable PII policy Governance → key → PII ON. Tune options if your plan exposes them (entity types, redact vs flag).
- Send a prompt with synthetic PII Use fake emails / phone numbers in a test message — never real customer data in screenshots.
- Inspect Flux IA Open the run: sensitive badge / PII occurrences. Optional: filter Flux IA « Sensibles uniquement ».
Pair with Cache/RAG carefully: order is fixed in the pipeline (see Concepts → Governed pipeline).